

Prerequisites
- Access to the Form Processing and Web Edge Sessions settings pages
- A subdomain already registered and active on Web Edge Sessions — bot protection can’t provision until a domain reaches this stage
How it decides who’s a bot
When a form requires a bot check, the script running on your page asks the visitor’s browser to prove it’s a real browser, not automated. Most visitors never see or do anything — the check runs silently in the background. A missing or invalid result gets the submission refused before it’s stored.Two switches, and both have to agree
Turning bot protection on for a form takes two settings, on two different pages:- Form Processing → Bot protection — the account-wide switch. Set to None, it cancels the check for every form, no matter what an individual form asks for.
- The form’s own settings — each form opts in separately. This is off by default.
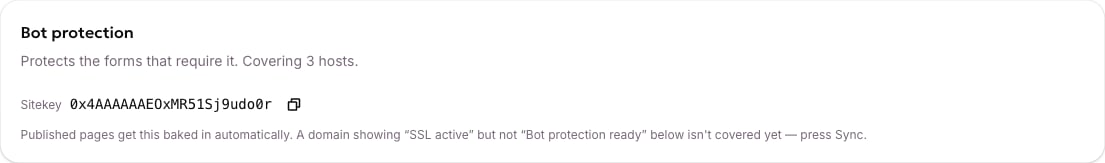
The Bot protection card, showing how many hosts the widget covers and the public sitekey.
Turn it on
1
Confirm your domain is active
On Web Edge Sessions, confirm the subdomain hosting your form shows State: active, with all four progress steps complete. Bot protection can’t provision on a domain that hasn’t finished this.
2
Sync to provision protection
Still on Web Edge Sessions, click Sync. This is also what extends bot protection to cover a newly added domain — it isn’t provisioned automatically the moment a domain goes active.
3
Turn on the account-wide switch
Open Form Processing, and set Bot protection to on.
4
Opt in the specific form
Open the form’s own settings and turn on its bot-check option.
If a submission is refused
- Every submission from the form is refused, and nothing else looks wrong. Confirm the form’s subdomain is active and synced — see the warning above.
- Some submissions succeed and others don’t. This is closer to the check working as intended; an occasional refusal from a slow connection or an older browser is expected, not a sign of misconfiguration.
- A developer manages your site’s security headers. If your site sets a Content Security Policy, it needs to allow Cloudflare’s challenge domain. Otherwise the bot-check widget never loads, and every submission is refused the same silent way. Loop in whoever manages your CSP; the exact directive is on the developer reference.
Related articles
- Set up Web Edge Sessions for your site
- Web Edge FAQ
- Need the exact mechanics — sitekey behavior, CSP directives, building the request yourself? See the developer reference.